VIK's contract is verified and publicly checkable today. We also publish automated security assessments, disclose material risk areas, and distinguish current facts from future security milestones.
Use the primary on-chain sources and published assessment platforms to verify the current state of VIK.
Deliberately ordered so risk is reduced at every step before real money moves.
VIK is deployed on Polygon PoS and the verified source code is publicly available on PolygonScan. The token has a fixed maximum supply of 24,000,000 VIK.
Audit Forge analyzed the deployed token contract using multiple automated security engines. The published automated assessment reports 98/100 — A / Robust / Low Risk, with 0 Critical, 0 High and 0 Medium findings. It also reports 10 Low and 34 Informational findings. This is an automated assessment, not a manual professional audit.
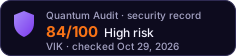
Quantum Audit's published snapshot dated 29 October 2026 reported a score of 84/100 — High Risk, with 1 High, 1 Medium and 4 Informational findings. It also flagged unlocked liquidity and low market liquidity. These are time-specific observations, not a permanent rating; liquidity, holder distribution and market activity can change.
A professional manual smart-contract review remains a future milestone. Automated assessments improve transparency and identify risks early, but they are not a substitute for a manual audit by a qualified security firm. Any future manual audit will be published publicly before being represented as a professional audit.
Liquidity security is separate from contract-code security. VIKASA will publish verifiable liquidity-lock information when liquidity is locked, including the relevant lock proof and on-chain details. No current liquidity-lock claim is made here unless it is independently verifiable on-chain.
The practical decisions behind the roadmap above.
VIK has a maximum supply of 24,000,000 tokens on Polygon PoS. The deployed token contract does not provide a mint function for increasing supply beyond the fixed cap.
VIK has published automated security assessments from Audit Forge and Quantum Audit. They evaluate different aspects and should be read together.
The contract source and on-chain token data can be independently checked on PolygonScan. Users do not need to rely only on statements made on this website.
Automated assessments do not eliminate risk. Liquidity, holder concentration, administrative control and market conditions can change after an assessment is published.
Liquidity security is tracked separately from contract-code security. Any future liquidity lock will be supported by publicly verifiable on-chain proof.
Technical documentation is published openly on GitHub, alongside the project's whitepaper and on-chain references.
Every claim on this page links to a primary source. Don't take our word for it — check.
Two automated assessments are published for transparency. They measure different risk dimensions and should not be presented as equivalent to a professional manual audit.
Automated multi-engine source-code analysis.
A · Robust · Low Risk
0 Critical · 0 High · 0 Medium
10 Low · 34 Informational
Automated contract, on-chain, holder and market-risk assessment.
Main flagged areas:
Liquidity lock status and market liquidity at the time of analysis.
The score is a time-specific on-chain snapshot and may change.
Audit Forge and Quantum Audit are automated security-assessment platforms. Their reports are useful for transparency and risk identification, but they are not professional manual smart-contract audits and do not guarantee that the contract or ecosystem is free from vulnerabilities. Quantum's risk score is a snapshot of on-chain conditions and can change as liquidity, holders and market activity change. VIK is a crypto asset and may be volatile or illiquid. It does not represent equity ownership or guarantee income, value, liquidity, or financial returns. This page is informational, not financial, legal, or investment advice. Verify contract, liquidity, holder and wallet data independently before making decisions. Never share a seed phrase or private key.
Our team responds to security and compliance inquiries directly — no ticket queue.